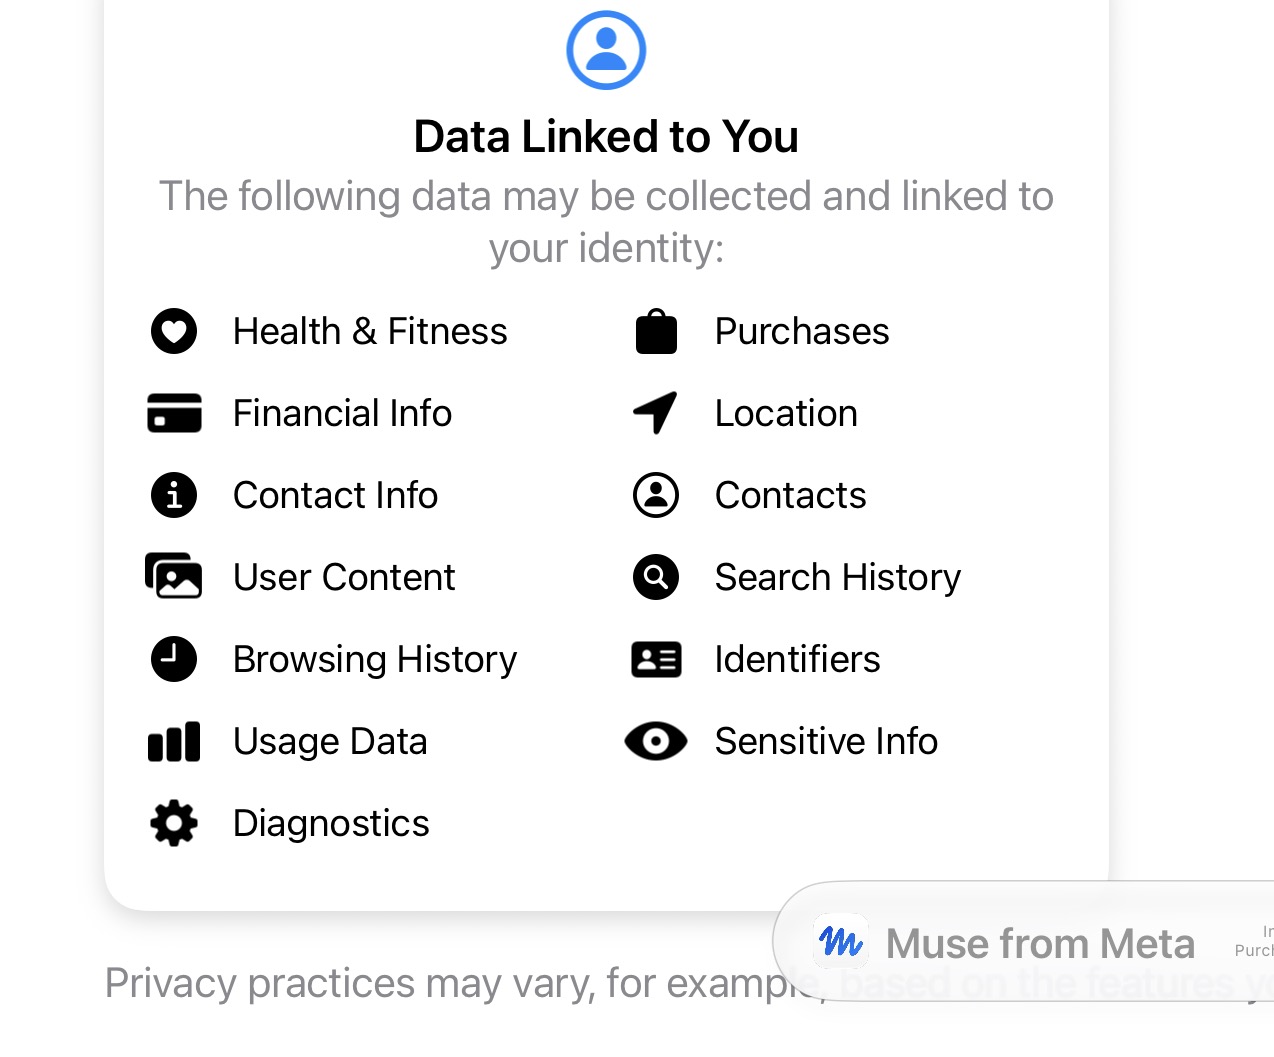
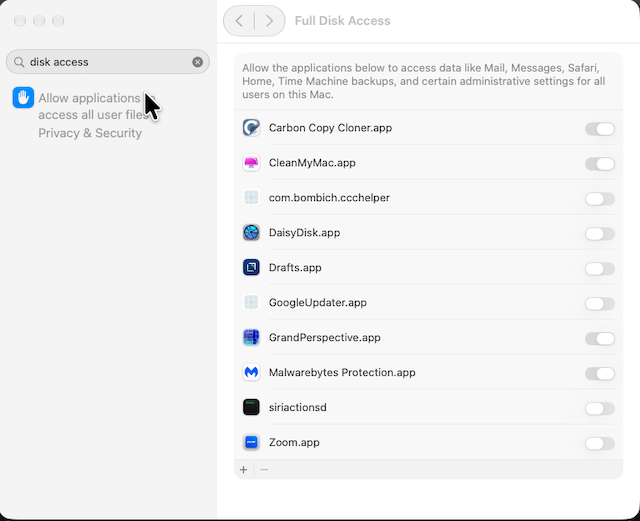
We give developers powerful APIs to build incredible capabilities into their apps for Apple products, backed by a set of controls designed to protect users’ private data. Full Disk Access largely sidesteps these controls in order to allow backup apps to function properly on the Mac. Some developers are using Full Disk Access in ways that could put users at risk, exposing everything on their systems—including files, mail, messages, and even browsing history—without users’ full knowledge and understanding. For communication apps, this can also compromise the privacy of the people users are communicating with.
Going forward, we will introduce additional controls to ensure that users who genuinely wish to grant an app this extraordinary level of access can only do so with very explicit user action. Addressing this is critical. As AI agents become increasingly capable and autonomous, the risks associated with this level of access will grow substantially. We are committed to ensuring users clearly understand these risks before granting such access, so they can make informed decisions about their own data and privacy.
I just hope I will still be able to grant an app I choose and trust full 100% unrestricted access to my file system if I so choose to do so. Without jumping through hoops. Or having to re-allow every single time, as if this were some Windows “are you really sure?” approach.
What would actually add value to me is to instead ban all the AI agents from doing what Apple alludes to above. I can already choose not to download such agents. And I do that. But the one thing I cannot do, is shut off and remove all Apple Intelligence stuff from Golden Gate.
So Apple, in an effort to prevent what you describe from happening, please give me a master toggle to turn off and remove all Apple Intelligence stuff installed with macOS. Thank you.
I was reviewing the apps I’ve given Full Disk Access permissions to on my Mac. They include:
Carbon Copy Cloner
ClamXAV
Find Any File
Terminal
With the exception of Terminal, these 3 are apps that I think novice – or certainly technically limited users – would still want to use.
They are certainly apps that a “technical user”, as John Gruber defines them, would want to use.
I hope that, however Apple redefines and/or adjusts the capabilities of how Full Disk Access is given, they don’t make it impossible (or heinously difficult) for developers who support the tools listed above to gain FDA privileges for their products.
BTW, interesting article on Ars Technica, about a purported incident that occurred with Meta’s Muse AI Agent, that may be associated with Apple’s decision to tighten/alter macOS’s Full Disk Access.
So far, only SuperDuper has Full Disk Access although several other apps (the Siri daemon, BB Edit, FireFox, FoxTrotProfessional, et cetera.) have asked.
That Arstechnica article links to a prior article that claims simply installing Muse on a Mac opens up a access to Messages and perhaps information in other apps as well. When questioned, Muse said that it wasn’t reviewing messages, but did pick up information on messages from Notifications – the writer didn’t authorize Muse accessing Notifications, either …
What I don’t know, and didn’t want to find out, is if Muse – installed on an iPhone – explicitly asks permission to access each of these things … or how it might otherwise get access to these things.
I checked my Full Disk Access settings and found something called “smbd” with no further explanation/ID with it. The other entries are recognizable app names.
Recently I did try to set up home networking over smb, could that be it?
The author of that article left me confused as to whether he did or did not give Muse Full Disk Access (FDA). He says he did not, but then illustrates that with a screenshot from Muse, not from Privacy & Settings. And his point (which apparently with this FDA update from Apple, Apple agrees with) is that even if he had, Muse (or similar app) needs to be more explicit about the breadth of that permission, and what they will do with it. I could be confused about his experience, but from a developer’s perspective, you can’t ask the OS for FDA. It must be explicitly granted by the user. All you can do is prompt the user to do so (and drop them off on the Privacy & Settings FDA doorstep, as it were). So if FDA was not granted, it is indeed a rather urgent mystery as to how Muse managed to read otherwise protected files.
I believe (though am not certain) that if you enable File Sharing on recent macOS versions, that means smb is enabled; and I believe the smbd app will then be running.
I have File Sharing enabled on Sequoia; but under System Settings → Privacy & Security → Full Disk Access, while smbd is listed, it is not enabled. (I believe this is because I said No to Full Disk Access, when I was queried by macOS.)
Yes, smbd is the Unix daemon (basically an “app” that is intended to run in the background) used for file sharing. Full disk access is normal if file sharing is or has been enabled.
Great! I can hardly wait for even more intrusive and irritating obstruction of processes running on my UNIX workstation OS when I least expect it. /S
There’s got to be some way for Apple to let power-users express that they are power-users. But Apple won’t bite because that would mean choice, and choice is baaaaaaaaad!
And yes, there’s some clearing up of the Muse Messages access story. I think Apple are right that users need protection from Meta of all companies, but if it’s really that bad then just raising the drawbridge isn’t going to stop a determined user. You need real gatekeeping, like iOS. Maybe they should make iOS/iPadOS more accommodating to those users, but realistically Macs have to be normie-proof as well and I think that means a much more radical per-installation tamper seal, which you can only break by erasing the device or something. It will always be possible to socially-engineer a user, no matter what Apple is thinking of.
Thanks @josehill , very helpful. I think I did share a whole volume when setting up the network and selected smb somewhere nearby in the settings. Maybe if you share only some folders in File Sharing this won’t turn on smbd in FDA.
Here is an article from Jeff Johnson, developer of Stop The Madness Pro including video of his installation of Meta Muse. He shows how Apple’s privacy is working as designed and Muse respects that. His conclusion is that the user ( journalist Jason Aten) misremembered what privileges he gave to Muse.
In my earlier comment, I should have mentioned that you can more specifically identify the items in the “Full Disk Access” settings pane by control-clicking or right-clicking on the item and choosing “Show in Finder”.
For example, if you do that with the smbd entry, a Finder window should open that shows that smbd is in the /usr/sbin directory. It is theoretically possible that a malicious actor might install a file called “smbd” in a different location, but I would expect that to be very rare.
In any case, unless you are absolutely 100% certain that you know what you are doing, you should not mess around in /usr/sbin, which is where macOS stores many important files essential to normal system operation.
I don’t recall Siri asking for permission, but at least it’s disabled here. [I do recall most of the others asking for permission – including Zoom, which I denied.
I don’t believe that’s correct. I routinely share such presentations in meetings but Zoom does not even show up in my Full Disk Access list. It does indeed show up under Screen & System Audio Recording, but only there. That makes sense since that is required to share. But full access to your disk it in general will not need so I’m not surprised to see it only show up where it does but definitely not in Full Disk Access (which is what the post you replied to is about).